RST Cloud Launches RST Breach Alert to Identify Which Leaked Credentials Are Still Active
Directory synchronisation checks exposed passwords against Active Directory, Microsoft Entra ID, and any LDAP
Press Release Disclaimer: This is a press release distributed through the XPR Media network. It has not been independently verified by our newsroom.
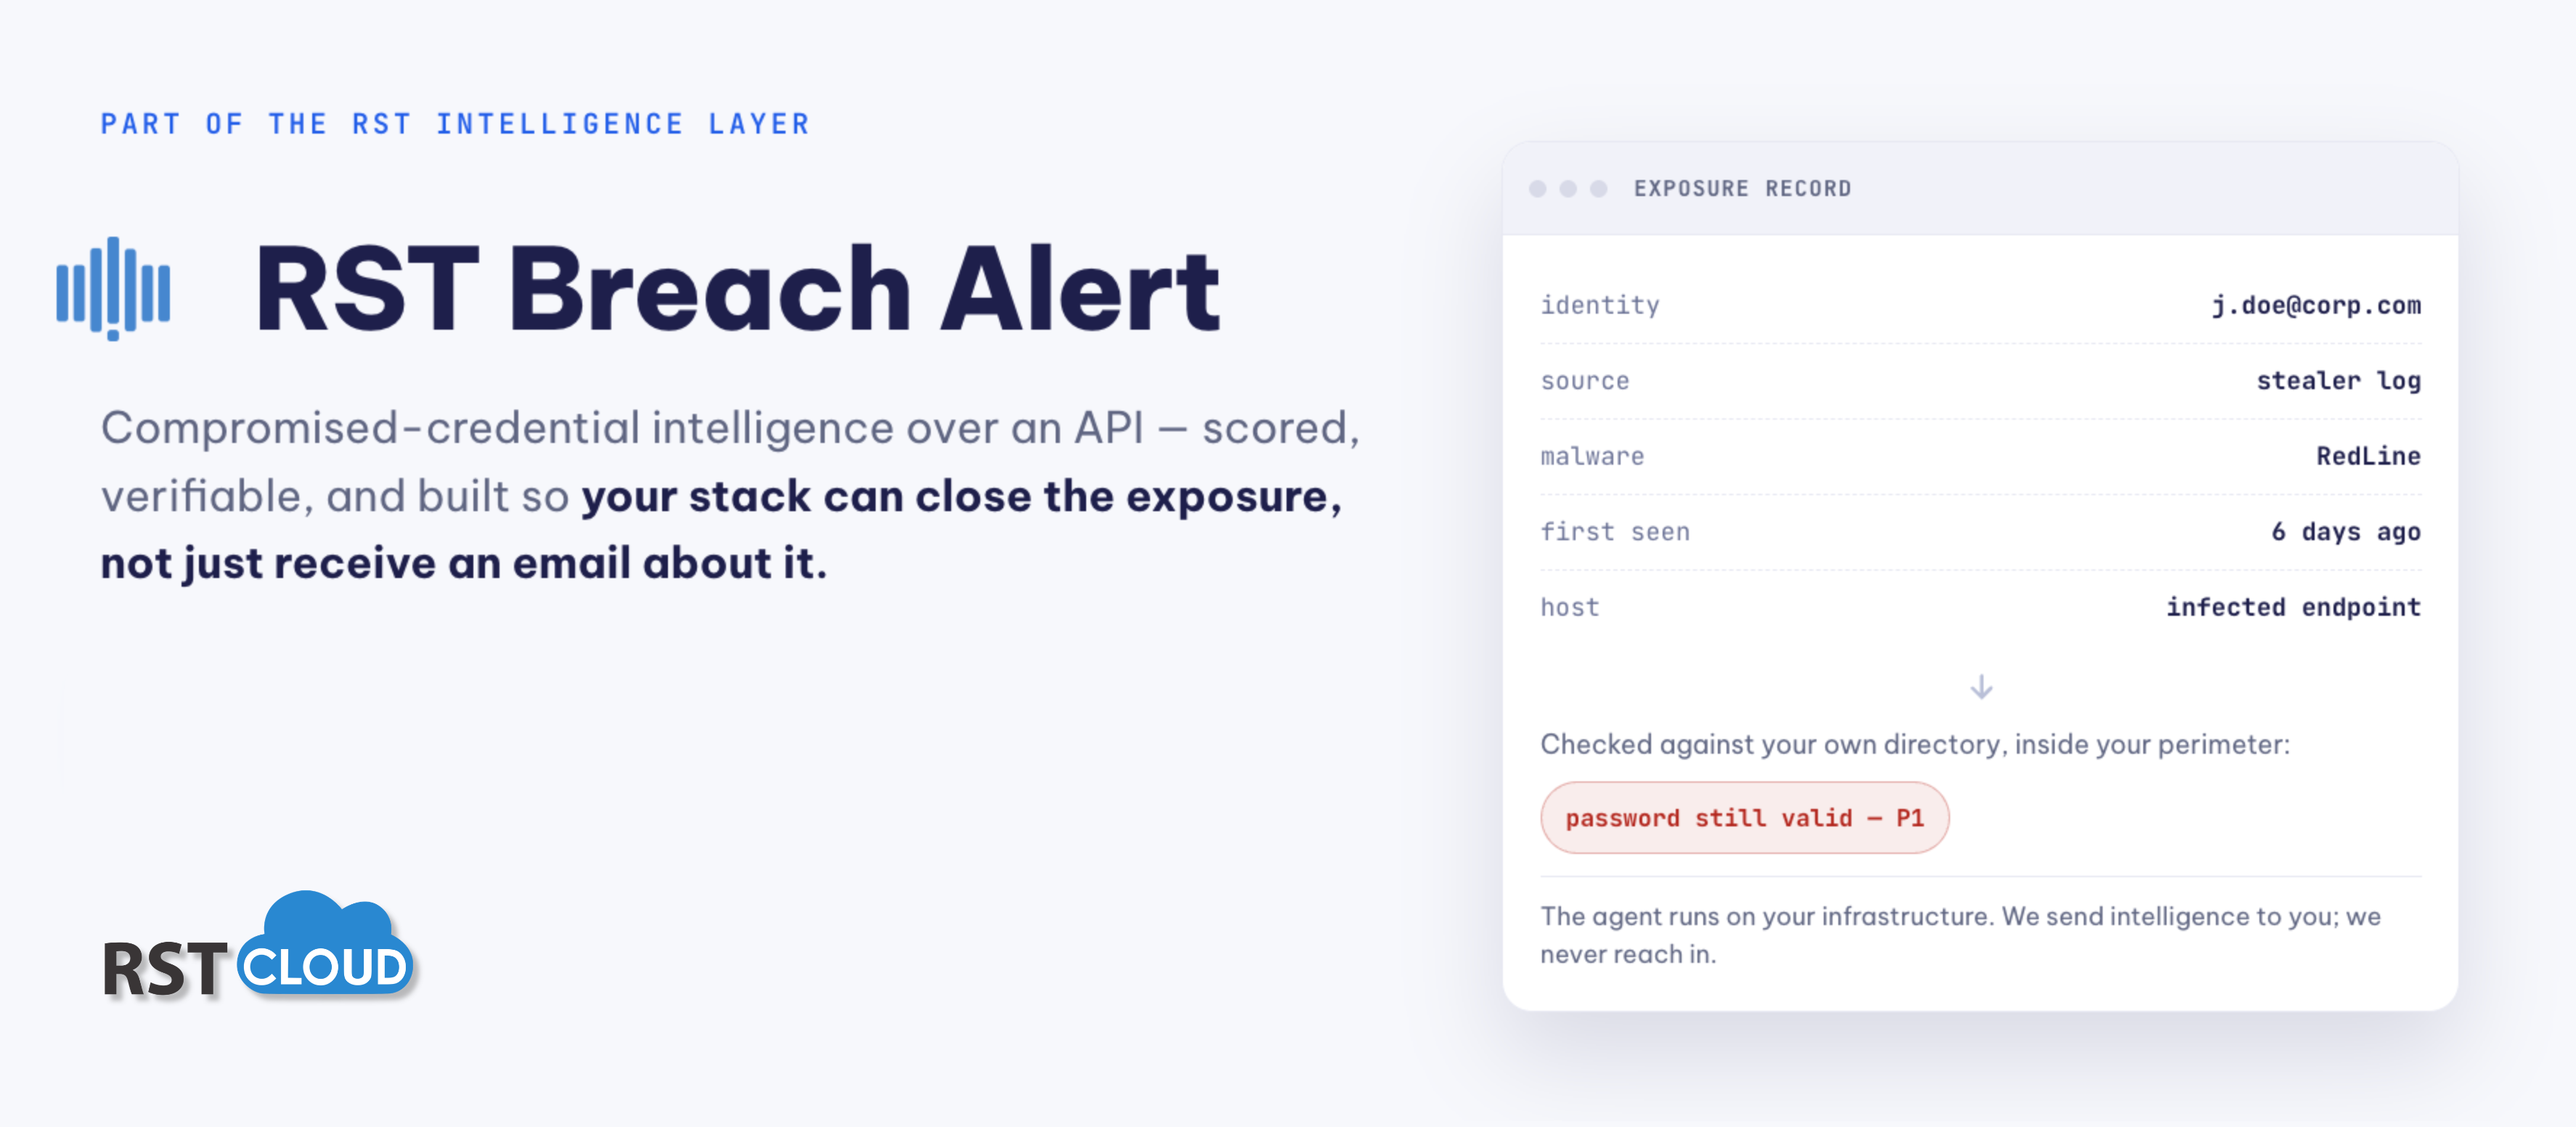

Directory synchronisation checks exposed passwords against Active Directory, Microsoft Entra ID, and any LDAP directory, automatically.
SYDNEY, NSW, AUSTRALIA, October 29, 2026 /EINPresswire.com/ — RST Cloud announced the launch of RST Breach Alert, a compromised-credential intelligence solution that helps organisations determine whether exposed employee credentials remain active or have already been changed. By validating breach intelligence against an organisation’s live directory, RST Breach Alert gives security teams the context they need to prioritise current risks and reduce unnecessary alerts.
“An alert tells you that a credential may be exposed. Directory synchronisation tells you whether it is actually a problem right now – whether it is still active and represents a current risk. That distinction turns a noisy feed into intelligence a SOC can act on with confidence.”
– Essa Amous, CTO, RST Cloud
From credential exposure to verified risk – RST Breach Alert continuously monitors compromised-credential intelligence to identify exposed corporate credentials. This intelligence is drawn from four main sources:
– Stealer logs: credentials, sessions and host context harvested by infostealer malware on infected endpoints.
– ULP files: URL-login-password combolists circulated in bulk across forums and channels.
– Data dumps: third-party breach databases, parsed and attributed back to identities.
– Leaks and paste sites: credential material published or traded in open and closed channels.
A lightweight, on-premises agent then validates findings against the organisation’s directory environment. By connecting external breach intelligence with current identity data, RST Breach Alert helps security teams distinguish between historical exposures and credentials that may still pose a security risk.
How It Works:
– Compromised-credential detection: continuously monitors threat intelligence for exposed corporate credentials and flags potential compromises.
– Live credential validation: checks exposed credentials against the organisation’s current directory environment to determine whether they are still active.
– Broad directory support: integrates with Microsoft Active Directory, Microsoft Entra ID and other LDAP-compatible directory services and more.
– Outbound-only architecture: a lightweight on-premises agent retrieves findings and performs validation locally, with no inbound network access required.
– Live-or-rotated verdict: determines whether an exposed password is still in use or has already been changed, taking password history into account where supported.
– Verified exposure data: raw credential details are released only for domains whose ownership the customer has verified.
RST Breach Alert combines two complementary scores to help security teams assess compromised credentials:
– Intrinsic alert score: evaluates the credibility and severity of the leaked data.
Remediation score: reflects the credential’s current status in the organisation’s directory environment.
– Together, these scores help teams prioritise findings based on both the significance of the exposure and the credential’s current status, rather than treating every leaked credential as an active threat.
Findings integrate with SOAR, SIEM and IAM workflows, helping teams streamline triage and remediation. Together, these capabilities reduce alert noise, improve risk prioritisation and accelerate incident response.
“In conversations with security teams, one limitation came up again and again: their compromised-credential monitoring could confirm whether a leaked password was still valid in a cloud directory such as Entra ID, but had no way to check local Active Directory or other LDAP-based directories. For organisations running hybrid or segmented environments, that means a significant share of their identity estate goes unverified. RST Breach Alert was designed around that problem, giving teams a consistent live-or-rotated verdict across every directory they rely on.”
– Anna Mikhailova, Director of Business Development, RST Cloud
RST Breach Alert is available now to new and existing RST Cloud customers, as well as trial participants. To request a trial, email trial@rstcloud.com or visit rstcloud.com/demo.
About RST Cloud
RST Cloud provides practical, machine-readable cyber threat intelligence for security operations teams and AI agents. Its API-first platform delivers threat intelligence feeds, indicators of compromise (IoC) lookups, noise suppression, and compromised-credential intelligence to help organisations detect, assess, and respond to cyber threats more effectively.
RST CLOUD PTY LTD
RST Cloud
Legal Disclaimer:
EIN Presswire provides this news content “as is” without warranty of any kind. We do not accept any responsibility or liability
for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this
article. If you have any complaints or copyright issues related to this article, kindly contact the author above.

Media gallery